N-00
Campus network, Faculty of Education EB1 and EB2
Two three-storey buildings, 722 peak users and 1,668 devices. A three-tier design with a core in each building and one firewall HA pair as the only Layer 3 point.
Status Design proposal Budget Build
A
Riser diagram
Sheet N-00/A Title Riser diagram Scale NTS
B
Design notes
Architecture
Three tiers with a core in each building, so EB1 needs two inter-building links instead of six.
The FortiGate 200F HA pair is the gateway for all 14 VLANs. Every switch is Layer 2.
Uplinks are 2×10G LACP: OM4 inside buildings, OS2 on two diverse paths between them.
Rapid-PVST+ with the EB2 core as root and Root Guard toward access. Sizing basis
APs per room = max(coverage, capacity). EB1302 needs 450 Mbps, so it gets 3 APs.
Highest PoE load is 73% of the switch budget, with 161 spare access ports.
One surviving uplink still carries the busiest floor (0.8 Gbps).
Firewall throughput 3 Gbps against 2.26 Gbps planned egress. Accepted trade-offs
EB2-F2-DS01 serves two floors; a second member would cost about THB 111,000.
One wireless controller; HA SSO would add about THB 140,000.
Two firewalls rather than one (+THB 388,500) to remove the single exit point.
N-01
Hierarchical physical topology
ITSC uplinks, firewall HA pair, two building cores, three distribution switches and six access stacks.
Scale NTS Links Tiers 3
Building EB2
EB2-MDF (server room, floor 1)
Building EB1
ITSC
University Core (campus L3)
EB2-MDF-FW01
FortiGate 200F (active)
OS2 10G
EB2-MDF-FW02
FortiGate 200F (passive)
OS2 10G
LEGEND
══════
OS2 single-mode, 10GBASE-LR
━━━━━━
OM4 multimode, 10GBASE-SR
─ ─ ─ ─
Cat6 U/UTP, 1G
· · · · ·
FortiGate HA heartbeat
HA
EB2-MDF-CS
C9300-24T x2, StackWise-480, NM-8X
OM4 10G
OM4 10G
EB2-MDF-WLC01
C9800-L-F
OM4 2x10G LACP
SERVERS
Servers / NVR (12 hosts)
Cat6 1G
EB2-F2-DS01
C9200L-24T-4X
OM4 2x10G LACP
EB2-F1-AS
3-switch stack
10 APs, 30 PC, 21 phone, 4 CCTV
OM4 2x10G LACP
EB1-F1-CS
C9200L-24T-4X x2 stack (EB1 core)
OS2 2x10G LACP
2 diverse paths
EB2-F2-AS
3-switch stack
9 APs, 41 PC, 21 phone, 3 CCTV
OM4 10G
+ Cat6 1G backup
EB2-F3-AS
3-switch stack
9 APs, 34 PC, 25 phone, 2 CCTV
OM4 10G
+ Cat6 1G backup
EB1-F2-DS01
C9200L-24T-4X
OM4 2x10G LACP
EB1-F3-DS01
C9200L-24T-4X
OM4 2x10G LACP
EB1-F1-AS
2-switch stack
9 APs, 16 PC, 12 phone, 3 CCTV
OM4 2x10G LACP
EB1-F2-AS
2-switch stack
11 APs, 15 PC, 13 phone, 3 CCTV
OM4 2x10G LACP
EB1-F3-AS
1-switch stack
9 APs, 3 PC, 1 phone, 2 CCTV
OM4 2x10G LACP
Sheet N-01 Title Physical topology Scale NTS
N-02
Addressing plan
10.10.0.0/16 faculty block, one /21 per building, summarised as 10.10.0.0/19. Gateway .1 on the firewall pair.
Summary 10.10.0.0/19 VLANs Gateway .1 HA VIP A
Address map
Sheet N-02/A Title Address map Scale 1 row = /21
B
Address lookup
C
VLAN schedule Filter
VLAN Name Scope Zone Subnet Gateway Endpoints Need Usable Headroom
N-03
Wireless
57 Cisco C9115AXI access points on a C9800-L-F controller. RSSI targets −65 dBm for lecture rooms and voice, −67 dBm for offices, −70 dBm for corridors; 20 MHz channels, 12 Mbps minimum rate.
APs Standard 802.11ax Controller C9800-L-F A
AP schedule by floor
Floor Users Wi-Fi devices APs Devices per AP
B
AP sizing 150 Mbps · 150 clients per AP
C
SSIDs
SSID Security VLAN EB1 / EB2
N-04
Security zones and policy
Each zone is the same VLAN group in both buildings. Policies are logged for 90 days (Computer Crime Act, s.26).
Default Deny Log 90 days Edge FortiGate HA A
Zone matrix
From \ to Internet Servers CCTV Management
Staff Allow, with IPS, AV and web filter Published services Admins to NVR only Admins only Student Allow, with IPS and app control Selected services Deny Deny Guest Internet only, web filter, rate cap Deny Deny Deny IoT DNS, NTP, vendor cloud Required only Deny Deny CCTV Deny NVR only Same zone Deny
Edge and wireless FortiGate NGFW HA: firewall, IPS, antivirus, web filter and application control. WPA3-Enterprise 802.1X with PMF; OWE with a captive portal for guests. Rogue AP detection on the controller. Access and management DHCP snooping, Dynamic ARP Inspection, BPDU Guard and Root Guard. Sticky port security on CCTV and IoT ports; unused ports shut in VLAN 999. SSH v2, HTTPS and SNMPv3 only, through VLAN 10.
N-05
Equipment and budget
All lines priced from supplier sources except fibre installation (estimate). Recurring after year three: AP and firewall licences.
Total VAT 7% Lines A
By category THB, before VAT
B
Bill of materials
Category Item Spec Qty Unit THB Line THB
N-06
Packet Tracer lab
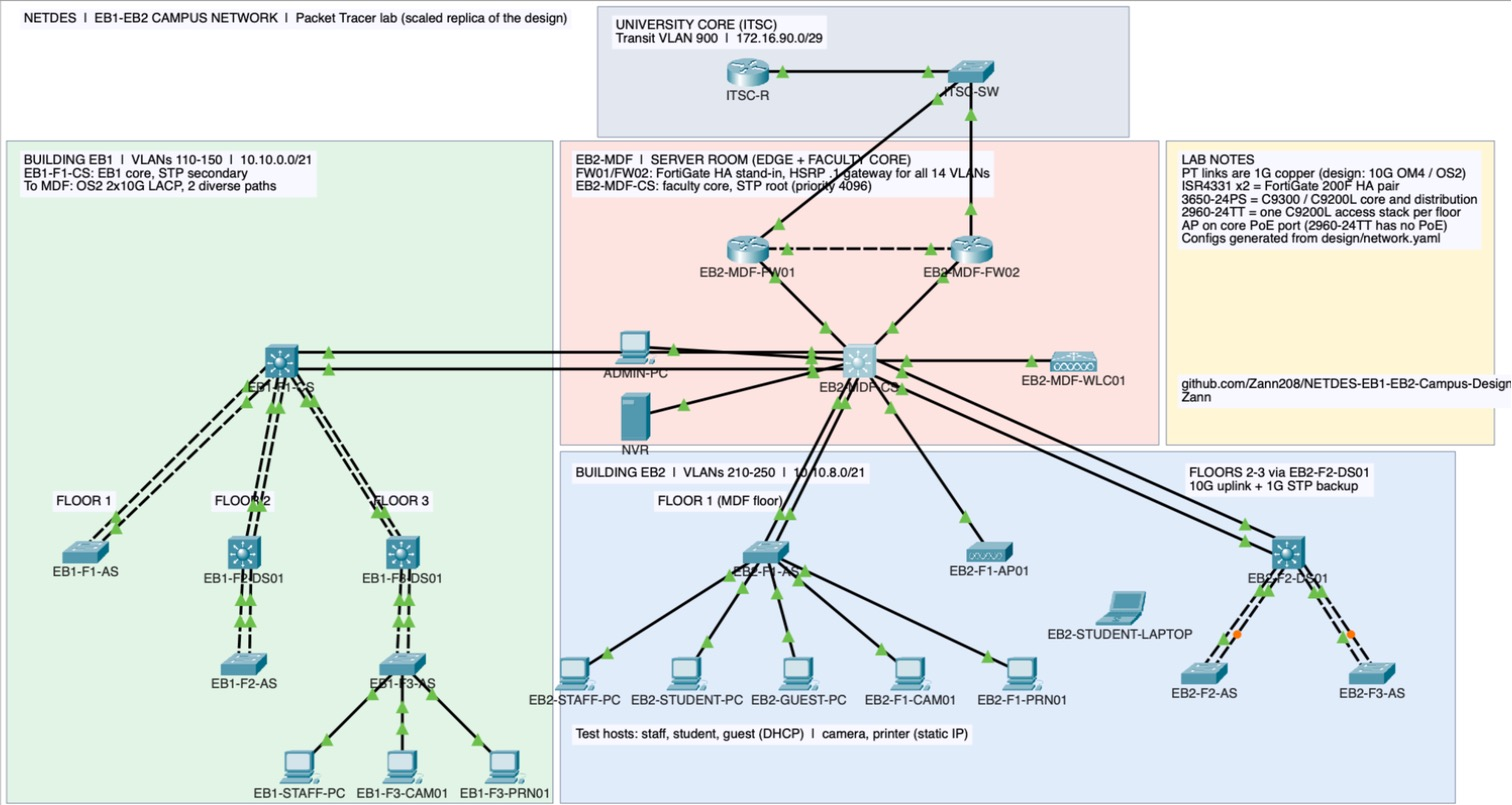
Scaled replica of the design: ISR4331 with HSRP for the FortiGate pair, 3650 for core and distribution, 2960 for each access stack.
Devices Tests Tool PT 9.0 A
Lab topology
B
Device configs
Device Copy config
C
Test plan
N-07
Design checks
Subnet sizing and overlap, ports, PoE, uplink failure, media limits, SFP+ budgets, controller scale and budget arithmetic.
Pass Warn Fail SectionAll sections ResultAll results PASS WARN FAIL